SOC 2

Prove your security and privacy controls
to your customers

A SOC 2 report evaluates an organization's information systems relevant to security, availability, processing integrity, confidentiality, and/or privacy. As a service provider, you need to assure your customers that your IT controls are aligned with, designed for, and applied to their own control objectives. Examinations are performed by both ControlCase IT and Cybersecurity experts and CPA accounting experts, and the report is signed off by registered CPAs, in good standing with State Board of Accountancy and that are registered for and participate in the AICPA Peer Review Program, while the wider ControlCase team brings the assessment experience built across PCI DSS, ISO 27001, and HITRUST.

Assess Once, Comply to Many

Assure Your Customers

Guarantee to your customers that your IT controls are aligned, designed, and applied effectively to their control objectives.

Benchmark Against Best Practices

Put your information systems up against recognized best practices for security, confidentiality of stored information, transaction processing integrity, system availability, and privacy of individuals’ personally identifiable information.

Reduce Outsourcing Risk

SOC reports give users the information they need to assess and address the risks associated with outsourcing services.

Choose the Right Report

SOC 2 is the correct option if you are asked for an assurance report that does not affect your clients' financial reporting.
What is a SOC 2 Report?

What is a SOC 2 Report?

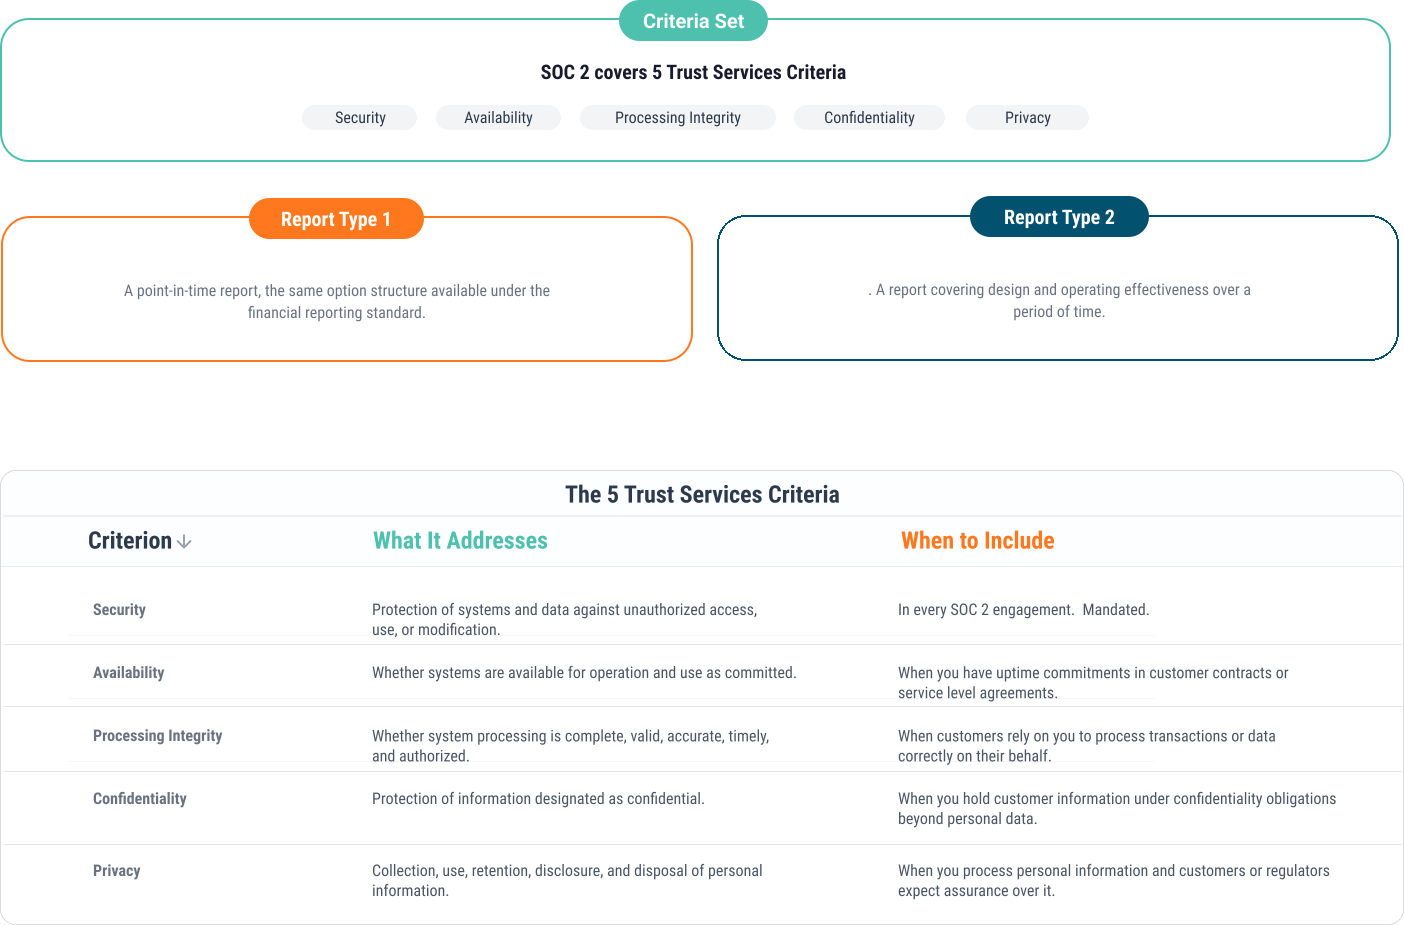
SOC 2 is an examination of controls at a service organization relevant to security, availability, processing integrity, confidentiality, or privacy. Unlike SOC 1, which addresses internal control over financial reporting, SOC 2 evaluates an organization's information systems against the Trust Services Criteria. System and Organization Controls is a suite of service offerings CPAs provide in connection with system-level controls of a service organization.

The AICPA created the SOC 2 reporting standard to serve organizations that were being asked for an assurance report but did not meet the criteria of the financial reporting standards. The AICPA established two SOC reporting options so service organizations can obtain the correct and recognizable third-party assurance report. Service providers that may impact the control environment of their clients' financial reporting activities should consider SOC 1 instead.

Who should obtain a SOC 2 report?

ControlCase serves candidates including hosting providers (web hosting, email hosting, data centers, document storage, backup service providers, cloud computing, dedicated server, network administrators), production printing (direct mail marketers, print and mail providers), Software as a Service (SaaS), Application Service Providers (ASP), health care service providers, and government service providers.

Why Choose ControlCase for SOC 2?

A CPA Partnership Built for Attestation Work
SOC 2 reports must be issued by licensed CPAs. ControlCase works hand-in-hand with our CPA partners to handle the attestation portion of SOC engagements by leveraging the Information Technology experts within ControlCase with the Accounting and Assurance experts who are CPAs, and the report comes from practitioners who are qualified to sign it.
Rigor Over Speed
The AICPA and the Journal of Accountancy warned through 2026 that quick-turn SOC engagements threaten the credibility of the report. A SOC 2 is only worth what your customers believe it is worth, and ControlCase, through its network of CPA partners, conducts the examination to the standard the report is meant to meet.
One Audit Across Your Framework Set
Most organizations that need a SOC 2 also carry, ISO 27001, PCI-DSS, and HITRUST obligations. ControlCase's technology offering, Compliance Hub, provides control mapping for other standards and regulations out of the box, so evidence gathered once supports multiple reports through the “One Audit” approach instead of running each engagement in isolation. Compliance Hub is part of the service offering at no additional cost.
A Dedicated Point of Contact
ControlCase assigns a named point of contact to each engagement who provides support and coordination from kickoff through report issuance, so you are not chasing status across teams.

Scoping Your SOC 2 Report

ControlCase SOC 2 Process

STEP 01
Scoping and Criteria Selection
Confirm that SOC 2 is the right report rather than SOC 1, solidify on Type I or Type II, and select which Trust Services Criteria are in scope beyond Security. Define the system boundary and assign your point of contact.
STEP 02
System Description Support
A SOC engagement rests on management's description of the system. ControlCase advises on structure and ultimate completeness, while the description is written by and remains management's own.
STEP 03
Examination Fieldwork
The CPA conducts the examination alongside your ControlCase assessor. For a Type 1 this tests the suitability of design as of the stated date. For a Type 2 it also tests operating effectiveness across the agreed review period.
STEP 04
Report Issuance
ControlCase issues via the CPA partner, the SOC 2 report with the practitioner's opinion, ready to share with customers and prospects under NDA, and agrees the timing of your next annual cycle.

Ready to Start Your SOC 2 Report?

Book Expert Time
Chat with an Advisor Available now
Chat with our representative
Compliance Advisor
Compliance Advisor HUMAN · LIVE
Online now · Replies within 2 minutes