Assess Once, Comply to Many


EU-Wide and Country-Specific Readiness
Address the common NIS2 baseline while accounting for applicable national transposition laws, authorities, registration requirements, and deadlines.

Strengthened Risk Management
Validate the cybersecurity measures required by Article 21, including incident handling, business continuity, supply-chain security, vulnerability management, cryptography, access control, asset management, and multifactor authentication.

Incident Reporting Readiness
Establish processes to identify, assess, escalate, and report significant incidents in accordance with NIS2 notification and reporting requirements.

Management Accountability
Support management-body approval, oversight, training, and evidence of governance over cybersecurity risk-management measures.
What is NIS2?
NIS2 also establishes cooperation and crisis-management mechanisms, including national Computer Security Incident Response Teams (CSIRTs), the NIS Cooperation Group, the CSIRTs Network, and EU-CyCLONe. On January 20, 2026, the European Commission proposed targeted amendments to clarify scope and jurisdiction, simplify certain obligations, and improve cross-border supervision. These amendments remain subject to the EU legislative process and should not be treated as current law until formally adopted and applicable.
National Implementation and Enforcement: NIS2 compliance is determined under each applicable Member State's transposition law. Organizations operating across the EU may face multiple competent authorities and country-specific rules. On July 8, 2026, the Commission referred Ireland, Spain, France, and the Netherlands to the Court of Justice of the EU for failing to notify complete transposition measures.
Why Choose ControlCase for NIS2 Assessment?
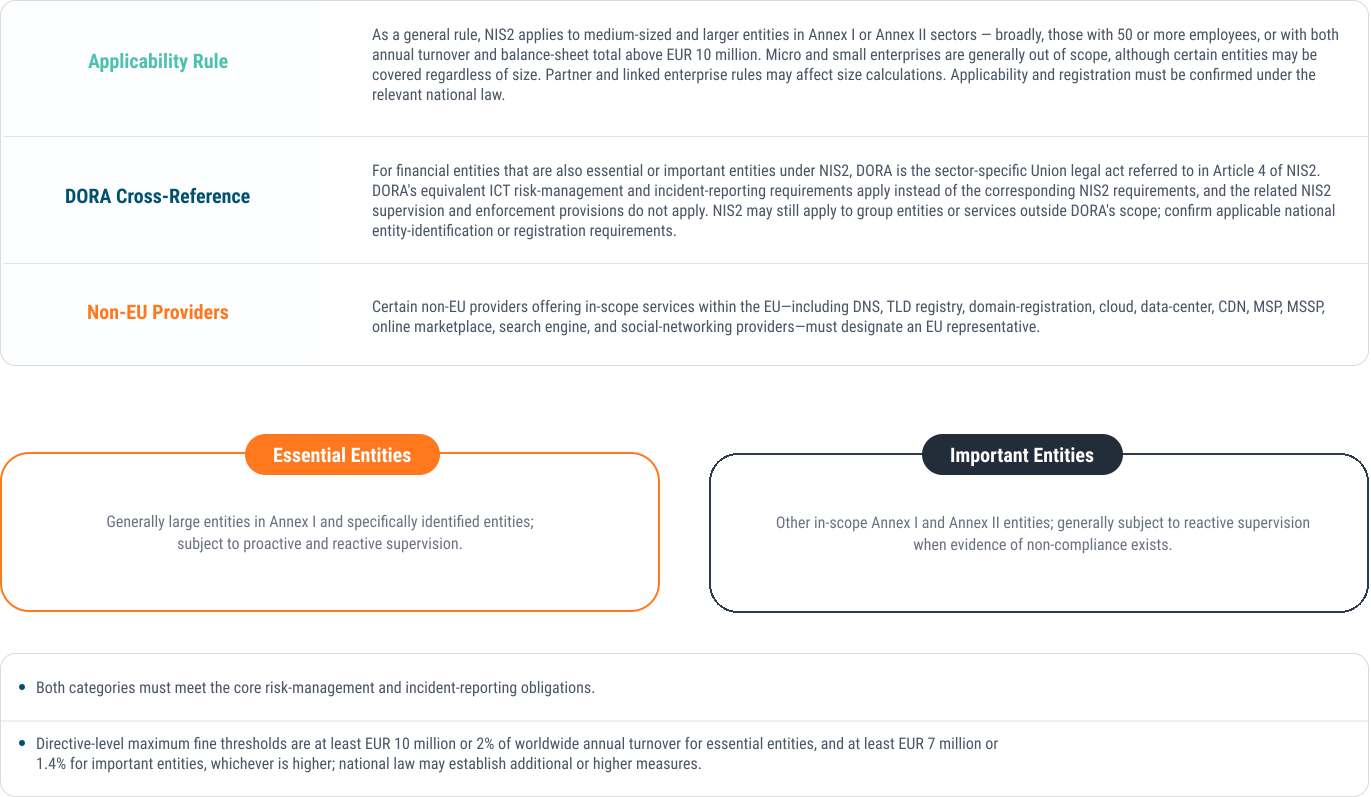
Who is in Scope for NIS2?
Energy; transport; banking; financial market infrastructures; health; drinking water; wastewater; digital infrastructure; ICT service management (business-to-business); public administration; and space.
Other Critical Sectors: Postal and courier services; waste management; manufacture, production, and distribution of chemicals; production, processing, and distribution of food; manufacturing of specified critical products; digital providers; and research.
ControlCase NIS2 Assessment Process