NIS2

Prepare your org for NIS2 compliance

The NIS2 Directive establishes an EU-wide cybersecurity baseline for essential and important entities across 18 critical sectors. It requires in-scope organizations to implement cybersecurity risk management measures, strengthen supply chain security, ensure management oversight, and report significant incidents. Because NIS2 is implemented through national law, applicability, registration, supervision, and enforcement must be assessed for each relevant Member State.
ControlCase provides NIS2 applicability, readiness, and gap assessments that combine the Directive's baseline requirements with applicable national transposition requirements. NIS2 is a regulatory compliance obligation, not a single EU certification.

Assess Once, Comply to Many

EU-Wide and Country-Specific Readiness

Address the common NIS2 baseline while accounting for applicable national transposition laws, authorities, registration requirements, and deadlines.

Strengthened Risk Management

Validate the cybersecurity measures required by Article 21, including incident handling, business continuity, supply-chain security, vulnerability management, cryptography, access control, asset management, and multifactor authentication.

Incident Reporting Readiness

Establish processes to identify, assess, escalate, and report significant incidents in accordance with NIS2 notification and reporting requirements.

Management Accountability

Support management-body approval, oversight, training, and evidence of governance over cybersecurity risk-management measures.
What is NIS2?

What is NIS2?

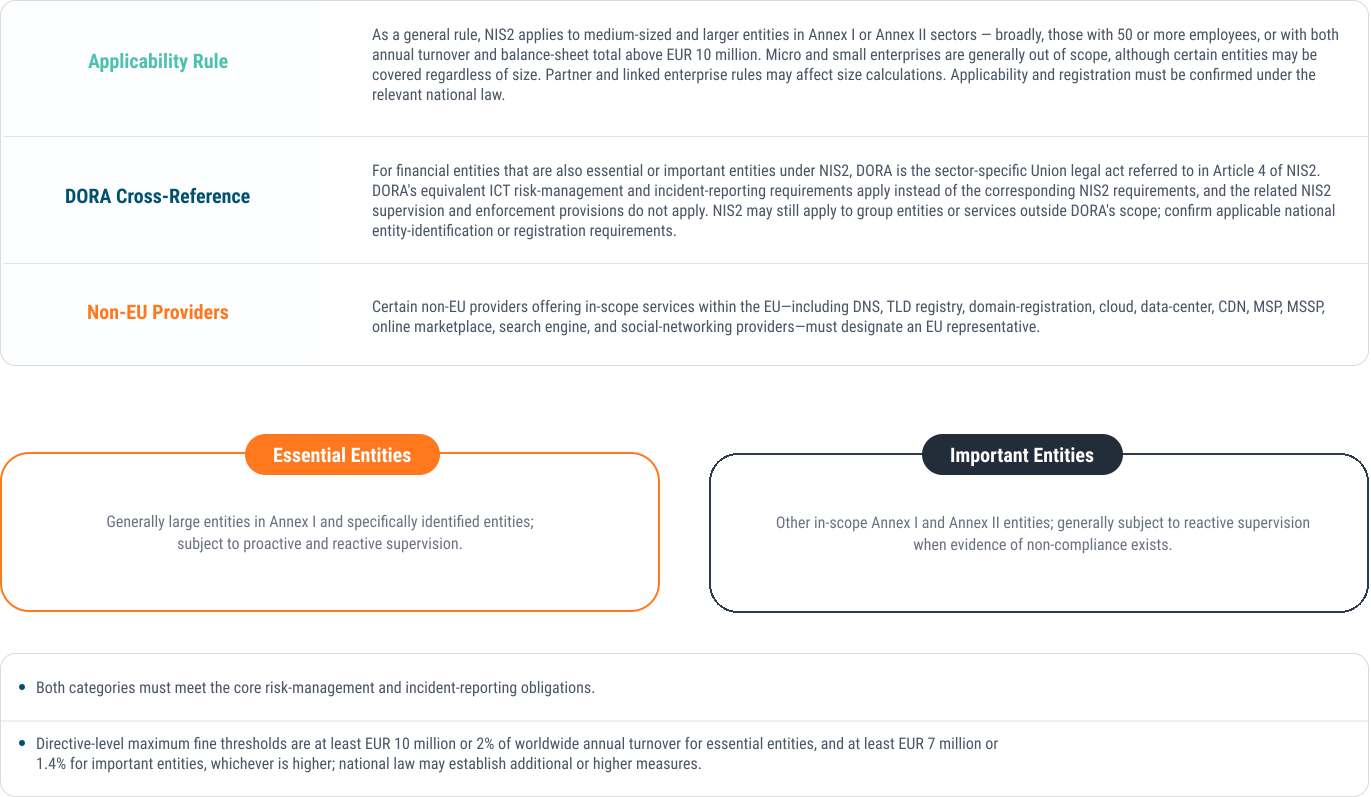
Directive (EU) 2022/2555, known as NIS2, replaced the original NIS Directive (EU) 2016/1148 and entered into force on January 16, 2023. Member States were required to transpose it into national law by October 17, 2024, and NIS1 was repealed from October 18, 2024. NIS2 expands the sectors and entities covered, strengthens cybersecurity risk management and incident reporting obligations, and introduces stronger supervision and enforcement.

NIS2 also establishes cooperation and crisis-management mechanisms, including national Computer Security Incident Response Teams (CSIRTs), the NIS Cooperation Group, the CSIRTs Network, and EU-CyCLONe. On January 20, 2026, the European Commission proposed targeted amendments to clarify scope and jurisdiction, simplify certain obligations, and improve cross-border supervision. These amendments remain subject to the EU legislative process and should not be treated as current law until formally adopted and applicable.

National Implementation and Enforcement: NIS2 compliance is determined under each applicable Member State's transposition law. Organizations operating across the EU may face multiple competent authorities and country-specific rules. On July 8, 2026, the Commission referred Ireland, Spain, France, and the Netherlands to the Court of Justice of the EU for failing to notify complete transposition measures.

Why Choose ControlCase for NIS2 Assessment?

One Audit™ Approach
Map NIS2 requirements to common controls and reuse applicable evidence across DORA, GDPR, ISO 27001, SOC 2, and other frameworks while maintaining NIS2-specific and country-specific compliance conclusions.
Regulatory and Technical Depth
Combine applicability and national regulatory mapping with governance review, interviews, evidence testing, Article 21 control validation, incident-reporting readiness, and supply-chain security assessment.
Compliance Hub Visibility
Centralize evidence, country-specific requirement mappings, findings, remediation status, and continuous compliance activities within ControlCase Compliance Hub.
Practical Remediation Support
Receive requirement-level conclusions, prioritized gaps, actionable recommendations, retesting, and support for national supervisory readiness from a global team with European presence.

Who is in Scope for NIS2?

Group 1
Annex I - Sectors of High Criticality

Energy; transport; banking; financial market infrastructures; health; drinking water; wastewater; digital infrastructure; ICT service management (business-to-business); public administration; and space.

Group 2
Annex II - Other Critical Sectors

Other Critical Sectors: Postal and courier services; waste management; manufacture, production, and distribution of chemicals; production, processing, and distribution of food; manufacturing of specified critical products; digital providers; and research.
ControlCase NIS2 Assessment Process

STEP 01
Applicability and Jurisdiction
Identify relevant legal entities, sectors, services, size thresholds, establishment locations, competent authorities, and national transposition laws.
STEP 02
Scope and Requirement Mapping
Classify essential or important entities and map the NIS2 baseline, applicable implementing rules, and national requirements.
STEP 03
Evidence Review and Interviews
Review governance, risk assessments, policies, incident processes, supplier controls, continuity plans, technical records, and supporting evidence.
STEP 04
Control and Technical Validation
Test selected Article 21 measures, incident-reporting readiness, management oversight, and samples across relevant systems, locations, and suppliers.
STEP 05
Gap Report and Remediation Roadmap
Provide requirement-level conclusions, country-specific gaps, risk rankings, recommendations, owners, and target dates.
STEP 06
Remediation Validation and Final Report
Retest corrective actions and issue the final NIS2 assessment report to support management, customer, and regulatory readiness.

Ready to Strengthen Your NIS2 Compliance Program?

Book Expert Time
Chat with an Advisor Available now
Chat with our representative
Compliance Advisor
Compliance Advisor HUMAN · LIVE
Online now · Replies within 2 minutes