Assess Once, Comply to Many


Foundation for FISMA and FedRAMP
NIST 800-53 serves as the information security standard for both FISMA and FedRAMP, so a single control program supports multiple federal requirements.

Security and Privacy in One Catalogue
Rev. 5 consolidates security and privacy controls into a single catalog, addressing both functionality and assurance.

Right-Sized to Your Systems
Security controls are scaled to your system’s FIPS 199 impact level, so you implement only what your system and mission require.

Maps to Other Frameworks
NIST publishes crosswalks from 800-53 Rev. 5 to the NIST Cybersecurity Framework, the Privacy Framework, and ISO/IEC 27001:2022, supporting an assess-once approach.
What is NIST SP 800-53?
NIST SP 800-53 provides a catalog of security and privacy controls for information systems and organizations, designed to protect organizational operations and assets, individuals, other organizations, and the Nation from threats, including hostile attacks, human errors, natural disasters, structural failures, foreign intelligence entities, and privacy risks. The controls are flexible and customizable, implemented as part of an organization-wide process to manage risk. NIST creates and promotes the standards federal agencies use to implement the Federal Information Security Management Act (FISMA).
The 20 control families: Access Control (AC), Awareness and Training (AT), Audit and Accountability (AU), Assessment, Authorization, and Monitoring (CA), Configuration Management (CM), Contingency Planning (CP), Identification and Authentication (IA), Incident Response (IR), Maintenance (MA), Media Protection (MP), Physical and Environmental Protection (PE), Planning (PL), Program Management (PM), Personnel Security (PS), PII Processing and Transparency (PT), Risk Assessment (RA), System and Services Acquisition (SA), System and Communications Protection (SC), System and Information Integrity (SI), and Supply Chain Risk Management (SR).
Why Choose ControlCase for NIST 800-53 Assessment?
ControlCase's Compliance Hub™ solution provides control mapping with other standards and regulations out of the box, so the evidence gathered for your NIST 800-53 assessment can be reused across your other compliance obligations through the One Audit approach.
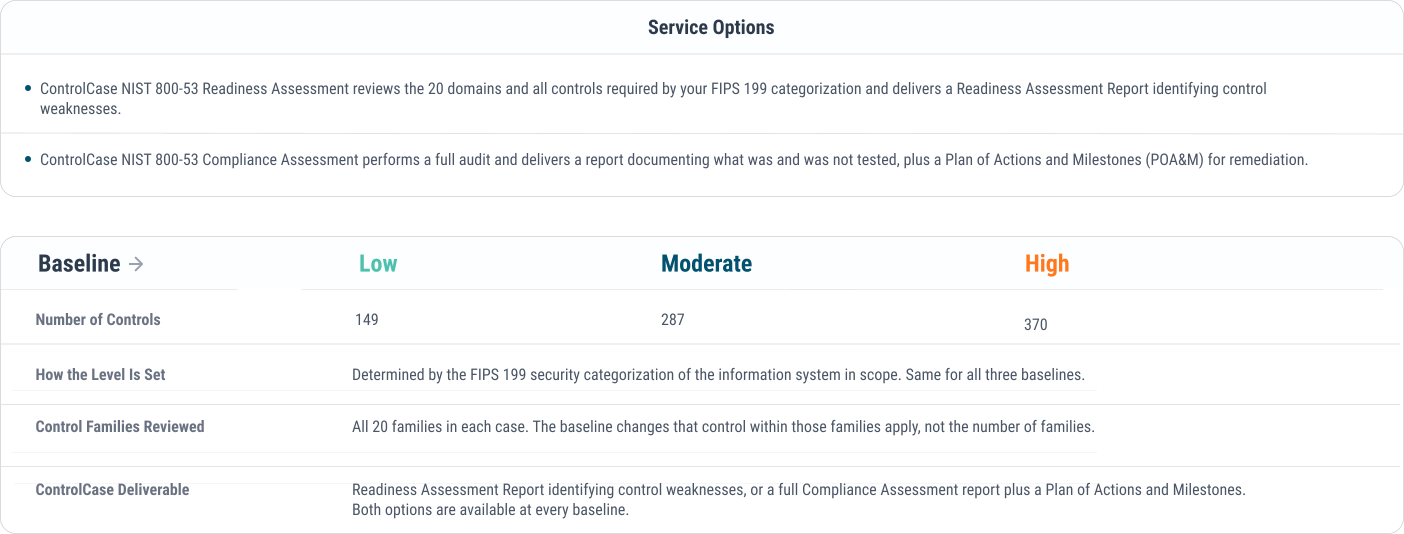
Which Baseline Applies to Your Systems?
149 controls, per ControlCase.
287 controls, per ControlCase.
370 controls, per ControlCase.
ControlCase NIST 800-53 Assessment Process