Assess Once, Comply to Many


Freely Distributable
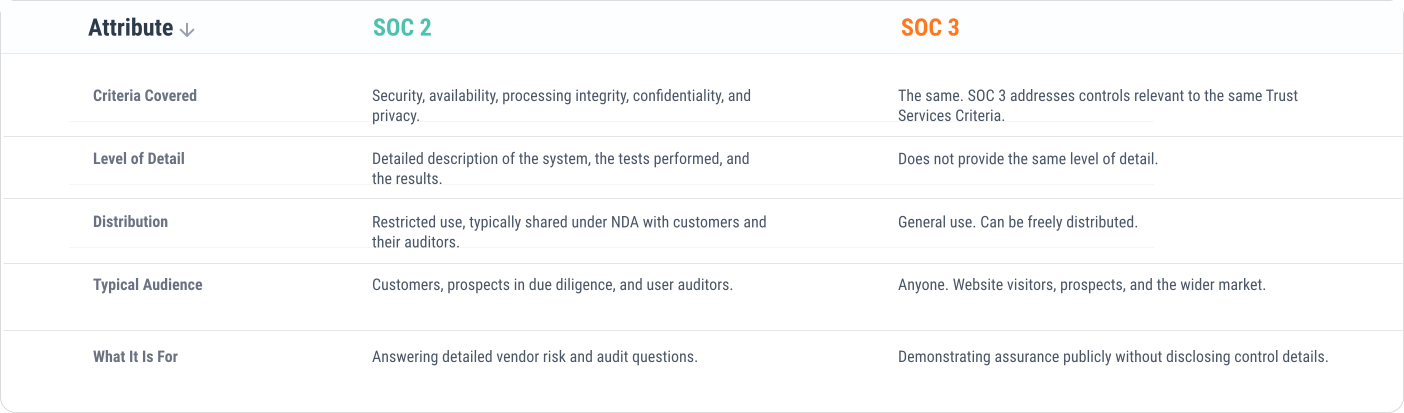
Because SOC 3 reports do not carry the same level of detail as SOC 2, they are considered general-use reports and can be freely distributed.

The SOC 3 is essentially a publicly accessible version of the SOC 2
SOC 3 addresses controls relevant to security, availability, processing integrity, confidentiality, and privacy, the same Trust Services Criteria that underpin a SOC 2, so your clients can preview your SOC 2 via the SOC 3.

A Recognized Standard
SOC 3 sits within the AICPA SOC suite alongside SOC 1 and SOC 2, so the assurance it provides is understood by buyers and their advisors.

Shorten Your Sales Cycle
A publishable report answers the security question before a prospect has to ask it, rather than waiting on an NDA to share a SOC 2.
What is a SOC 3 Report?
In practice, this means the two reports serve different audiences from the same underlying work. A SOC 2 gives your customers and their auditors a detailed description of your system, the tests performed, and the results. A SOC 3 provides everyone else with the practitioner's opinion without the underlying details. AICPA publishes an Illustrative SOC 3 Report showing the expected form, and its CPE catalog treats SOC 2 and SOC 3 planning, execution, and reporting as a single subject.
Why Choose ControlCase for SOC 3?
Where SOC 3 Fits
Appropriate when your customers and their auditors require detailed assurance, and you have no need for a publishable report.
The common pairing. SOC 2 satisfies customer due diligence under an NDA, and SOC 3 gives sales and marketing something to publish.
ControlCase SOC 3 Process