NPT

Find Out How Far an Attacker
Gets Inside Your Network

ControlCase NETWORK PENETRATION TESTING simulates real-world attacks against your external perimeter, internal network, remote access paths and cloud infrastructure. Findings are manually verified, chained into realistic attack paths and prioritized by business impact.

Assess Once, Comply to Many

Real-World Assurance

Findings are exploited and validated rather than reported from a scanner, so remediation effort goes to exposures attackers reach and exploit.

Attack Path Visibility

Results show how a low-severity exposure becomes domain compromise, so you break the chain at the cheapest point instead of patching everything at once.

Independent Verification

An objective assessment of how perimeter, segmentation, identity and monitoring controls perform under attack conditions.

Audit-Ready Evidence

Methodology, scope, findings, segmentation results and re-test closure are documented in the form assessors expect for PCI DSS, ISO 27001, SOC 2, HIPAA and Indian regulatory requirements.
What is Network Penetration Testing?

What is Network Penetration Testing?

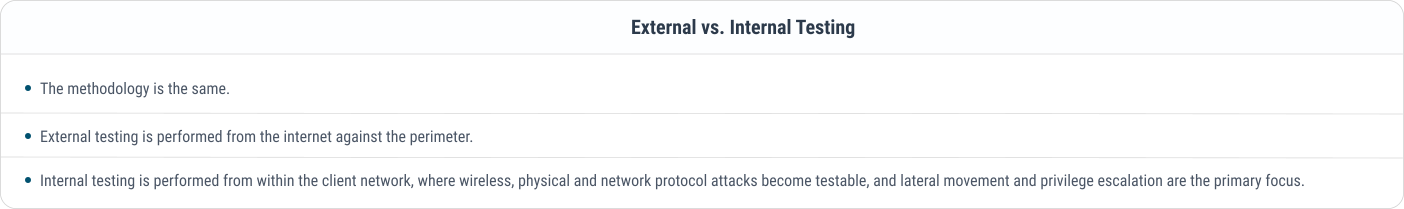
A network penetration test is a controlled, authorized simulation of real-world attacks against your network infrastructure. A vulnerability scan reports what might be exploitable. A penetration test establishes which hosts an attacker compromises, which credentials they obtain, how far they move laterally and which sensitive environments they reach. Most breaches of internal environments follow this pattern: an initial foothold, then credential harvesting, privilege escalation and lateral movement across a flat or weakly segmented network.

PCI DSS v4.0.1 Requirements 11.4.1 to 11.4.4 require an industry-accepted testing methodology, internal and external penetration testing at least once every 12 months and after significant change, and correction and re-testing of exploitable findings. Requirements 11.4.5 and 11.4.6 add segmentation testing at least every 12 months, or every six months for service providers. ISO/IEC 27001:2022, HIPAA and HITRUST, SOC 2, NIST CSF 2.0, NIST SP 800-115, and RBI, SEBI CSCRF and CERT-In requirements set comparable expectations.

What We Test

  • External penetration test: Internet-facing IP ranges, perimeter devices, published services, remote access gateways, VPN and mail infrastructure, and externally reachable management interfaces.
  • Internal penetration test: Corporate LAN, data centre and server segments, network devices, endpoints and the Active Directory or identity estate, simulating a malicious insider or an attacker with an established foothold.
  • Cloud and hybrid infrastructure: Exposed services, network security groups, instance metadata exposure, identity misconfiguration and on-premises to cloud trust paths.
  • Remote access and VPN: VPN concentrators, SSL-VPN portals, RDP and jump host exposure, multi-factor authentication implementation and split-tunnel configuration.

Why Choose ControlCase for Network Penetration Testing?

Credentialed, Experienced Testers
A dedicated team of information security professionals with recognized industry credentials and experience across banking, payments, healthcare, technology and retail. Every engagement is subject to internal quality review before findings are released.
High-Risk Findings Shared as Confirmed
High-risk findings are communicated as they are confirmed rather than held for the final report, so urgent exposures close while testing is still in progress.
Flexible Delivery Model
External testing is delivered remotely from the ControlCase Security Center of Excellence in Mumbai, India. For internal, segmentation, wireless and physical testing, consultants deploy on site or connect through a controlled testing appliance or jump host.
Methodology Mapped to MITRE ATT&CK
Built on OSSTMM, PTES, NIST SP 800-115 and PCI SSC Penetration Testing Guidance. Attack paths map to MITRE ATT&CK, so you compare what testers did against what your monitoring detected.
Lab-Validated Exploit Library
ControlCase maintains a curated library of exploits and vulnerability intelligence. New exploits are validated in an internal lab against test targets before use in a client engagement, avoiding undesirable side effects on production systems.

Testing Perspectives

The perspective is agreed during scoping. Every engagement uses automated tooling for coverage and manual testing for exploitation, chaining and validation.

Approach 1
Zero Knowledge
(Black Box)

Description: No background information or credentials. Only the in-scope IP addresses or ranges are provided.

Key areas: How much information the organization exposes about itself.

Applies to: Reproducing the viewpoint of a complete outsider.

Approach 2
Informed
(Grey Box)

Description: Network architecture, target systems, operating system and application information, plus a standard user account for internal tests.

Key areas: Broader coverage in a fixed test window.

Applies to: Mirroring a realistic attacker with some knowledge or an already compromised user.

Approach 3
Full Knowledge
(White Box)

Description: Architecture diagrams, firewall rule sets and device configurations alongside credentials.

Key areas: The deepest coverage and the most precise remediation guidance.

Applies to: Segmentation validation.
ControlCase Network Penetration Testing Process

STEP 01
Scoping and Rules of Engagement
ControlCase inventories in-scope IP addresses, ranges and domains, and documents test windows, permitted techniques, prohibited actions and success objectives in writing. Only client-nominated addresses are tested, so supplier, partner and ISP systems are never inadvertently included.
STEP 02
Discovery and Confirmation
ControlCase maps live hosts, open ports, services, operating systems and certificates, plus open-source intelligence for external tests. Results are reviewed with your team, and unexpected hosts are raised for a scoping decision, surfacing forgotten and unmanaged assets.
STEP 03
Vulnerability Identification
Authenticated and unauthenticated scanning is tuned to your environment to limit noise and operational risk. Results are triaged and manually validated into a prioritized list of candidate attack vectors, not a raw scanner export.
STEP 04
Exploitation and Lateral Movement
Testers exploit validated weaknesses across patching, configuration, network protocols, credentials, Active Directory, remote access, encryption and cloud. Where a foothold is achieved, ControlCase demonstrates privilege escalation and lateral movement toward agreed objectives. No sensitive data is exfiltrated.
STEP 05
Reporting
Findings include severity, affected hosts, reproduction steps, evidence, business impact and remediation guidance. Attack paths are presented end to end, so the single control failure enabling a chain gets priority. Results publish to your secure ControlCase portal.
STEP 06
Remediation Support and Re-Test
ControlCase advises your infrastructure teams during remediation, re-tests exploitable findings and issues a closure report, the evidence required by PCI DSS Requirement 11.4.4.

Ready to Test Your Network Defenses?

Book Expert Time
Chat with an Advisor Available now
Chat with our representative
Compliance Advisor
Compliance Advisor HUMAN · LIVE
Online now · Replies within 2 minutes