Assess Once, Comply to Many


Real-World Assurance
Findings are exploited and validated rather than reported from a scanner, so remediation effort goes to exposures attackers reach and exploit.

Attack Path Visibility
Results show how a low-severity exposure becomes domain compromise, so you break the chain at the cheapest point instead of patching everything at once.

Independent Verification
An objective assessment of how perimeter, segmentation, identity and monitoring controls perform under attack conditions.

Audit-Ready Evidence
Methodology, scope, findings, segmentation results and re-test closure are documented in the form assessors expect for PCI DSS, ISO 27001, SOC 2, HIPAA and Indian regulatory requirements.
What is Network Penetration Testing?
PCI DSS v4.0.1 Requirements 11.4.1 to 11.4.4 require an industry-accepted testing methodology, internal and external penetration testing at least once every 12 months and after significant change, and correction and re-testing of exploitable findings. Requirements 11.4.5 and 11.4.6 add segmentation testing at least every 12 months, or every six months for service providers. ISO/IEC 27001:2022, HIPAA and HITRUST, SOC 2, NIST CSF 2.0, NIST SP 800-115, and RBI, SEBI CSCRF and CERT-In requirements set comparable expectations.
What We Test
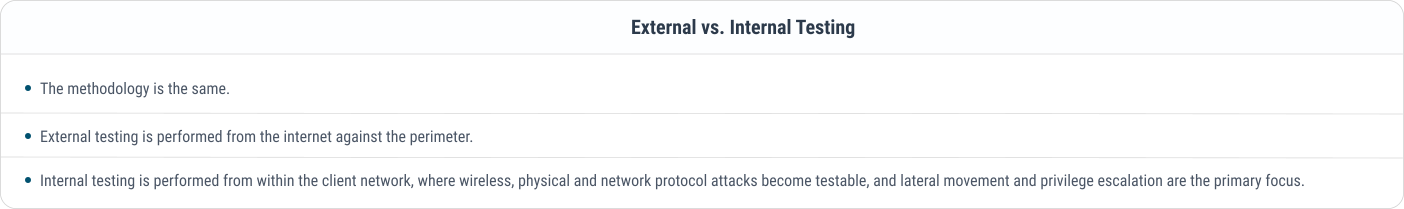
- External penetration test: Internet-facing IP ranges, perimeter devices, published services, remote access gateways, VPN and mail infrastructure, and externally reachable management interfaces.
- Internal penetration test: Corporate LAN, data centre and server segments, network devices, endpoints and the Active Directory or identity estate, simulating a malicious insider or an attacker with an established foothold.
- Cloud and hybrid infrastructure: Exposed services, network security groups, instance metadata exposure, identity misconfiguration and on-premises to cloud trust paths.
- Remote access and VPN: VPN concentrators, SSL-VPN portals, RDP and jump host exposure, multi-factor authentication implementation and split-tunnel configuration.
Why Choose ControlCase for Network Penetration Testing?
Testing Perspectives
The perspective is agreed during scoping. Every engagement uses automated tooling for coverage and manual testing for exploitation, chaining and validation.
(Black Box)
Description: No background information or credentials. Only the in-scope IP addresses or ranges are provided.
Key areas: How much information the organization exposes about itself.
Applies to: Reproducing the viewpoint of a complete outsider.
(Grey Box)
Description: Network architecture, target systems, operating system and application information, plus a standard user account for internal tests.
Key areas: Broader coverage in a fixed test window.
Applies to: Mirroring a realistic attacker with some knowledge or an already compromised user.
(White Box)
Description: Architecture diagrams, firewall rule sets and device configurations alongside credentials.
Key areas: The deepest coverage and the most precise remediation guidance.
Applies to: Segmentation validation.
ControlCase Network Penetration Testing Process