APT

Validate Application Security
Before an Adversary Does

ControlCase APPLICATION PENETRATION TESTING simulates real-world attacks against your web, API, mobile, desktop and cloud-native applications. Every finding is manually verified, prioritized by business impact and documented as audit-ready evidence for PCI DSS, ISO 27001, SOC 2 and HIPAA.

Assess Once, Comply to Many

Real-World Assurance

Findings are manually validated and exploited rather than reported from a scanner, so your remediation effort goes to issues attackers exploit.

Coverage Beyond the Network Perimeter

Testing addresses access control, session, logic and API weaknesses firewalls, patch management and vulnerability scanning do not detect.

Audit-Ready Evidence

Methodology, scope, findings and re-test closure are documented in the form assessors expect for PCI DSS, ISO 27001, SOC 2, HIPAA and Indian regulatory requirements.

One Compliance Partner

Combine penetration testing with ControlCase compliance and certification programs to reduce duplicated effort and evidence collection across audits.
What is Application Penetration Testing?

What is Application Penetration Testing?

An application penetration test is a controlled, authorized simulation of real-world attacks against an application to identify, exploit and validate security weaknesses before an adversary does. It goes beyond automated scanning. Findings are manually verified, chained where possible to demonstrate business impact, and prioritized so your team directs remediation effort at the exposures putting cardholder data, personal data, health records, intellectual property and authentication material at risk.

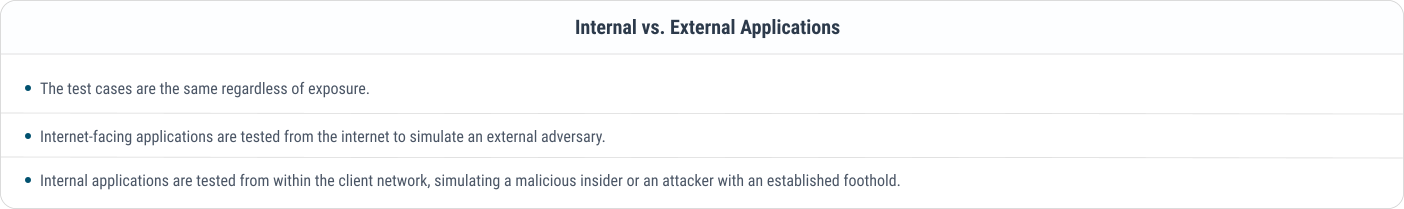
Independent application testing is a requirement under most security standards and regulations. PCI DSS v4.0.1 Requirements 11.4.1 to 11.4.4 call for a defined penetration testing methodology, internal and external penetration testing at least once every 12 months and after significant change, and correction and re-testing of exploitable findings. ISO/IEC 27001:2022, HIPAA and HITRUST, SOC 2, GDPR, the India DPDP Act 2023, and RBI, SEBI CSCRF and CERT-In requirements set comparable expectations.

What We Test

  • Web applications: Traditional server-rendered applications, single-page applications, admin and back-office consoles, customer and partner portals.
  • APIs and web services: REST, SOAP, GraphQL and gRPC interfaces, including undocumented, versioned and machine-to-machine endpoints.
  • Mobile applications: Android and iOS clients, covering the application binary, local data storage, platform interaction and supporting backend services.
  • Thick client and desktop: Client-server and installed desktop applications, including local privilege, storage and traffic interception testing.
  • Cloud-native workloads: Application-layer testing of containerized and serverless services, including exposed management interfaces and inter-service authorization.
  • AI and LLM-enabled features (optional): Prompt injection, insecure output handling, excessive agency and data leakage in applications with integrated language models.

Why Choose ControlCase for Application Penetration Testing?

Credentialed, Experienced Testers
A dedicated team of information security professionals with recognized industry credentials and experience across banking, payments, healthcare, technology and retail. Internal quality review supports every stage of the engagement.
Standards-Based Methodology
Built on OWASP Top 10:2025, OWASP API Security Top 10:2023, OWASP WSTG v4.2, OWASP ASVS 5.0.0, OWASP MASVS and MASTG, PTES and NIST SP 800-115, so you and your assessor trace what was tested and why.
Continuous Visibility Through the GRC Platform
The ControlCase GRC platform holds scope, evidence, findings and remediation tracking in one secure repository. You see engagement progress, finding status and closure evidence throughout, not only in a final report.
Global Delivery Model
Testing is delivered from the ControlCase Security Center of Excellence, with consultants deployed on site where internal applications or restricted environments require it. This reduces travel and logistical cost without compromising depth of testing.
Lab-Validated Exploit Library
ControlCase maintains a curated library of exploits and vulnerability intelligence. New exploits are validated in an internal lab against test targets before use in a client engagement, avoiding undesirable side effects on production systems.

Testing Perspectives

The approach is agreed during scoping and usually combines the perspectives below. Every engagement uses automated tooling for coverage and manual testing for exploitation, chaining and business logic.

Approach 1
Black Box

Description: No prior knowledge of the application, its architecture or its deployment.

Key areas: Discovering and attacking the application from the outside.

Applies to: Simulating an unauthenticated external attacker.

Approach 2
Grey Box (Recommended Default)

Description: Valid credentials for each application role, plus basic architecture and platform information.

Key areas: Authenticated attack surface, horizontal and vertical privilege escalation, and business logic flaws.

Applies to: Most engagements. This is the recommended default.

Approach 3
White Box

Description: Credentials plus design documentation, API specifications and, where agreed, source code access.

Key areas: The deepest coverage and the most precise remediation guidance.

Applies to: Engagements where design documentation, API specifications or source code are available.
ControlCase Application Penetration Testing Process

STEP 01
Scoping and Rules of Engagement
ControlCase confirms target applications, roles, environments, test windows, permitted techniques, escalation contacts and out-of-scope conditions. Authorization, methodology and scope are documented in writing as evidence for your assessor.
STEP 02
Reconnaissance and Discovery
ControlCase enumerates technologies and versions, exposed endpoints and subdomains, authentication flows, API surface, client-side scripts and third-party integrations.
STEP 03
Vulnerability Identification and Manual Testing
Authenticated and unauthenticated testing covers configuration, authentication, authorization, session management, injection, cryptography, business logic, client-side, API, mobile and supply chain modules. Every automated result is manually validated, and false positives are removed before reporting.
STEP 04
Exploitation and Validation
Weaknesses are safely exploited to confirm business impact and, where permitted, chained into realistic attack paths. All activity is logged, non-destructive by default and bounded by the agreed rules of engagement.
STEP 05
Reporting
Findings include severity, affected components, reproduction steps, evidence, business impact and remediation guidance mapped to CWE and OWASP. Results publish to your secure ControlCase portal and remediation tracking module.
STEP 06
Remediation Support and Re-Test
ControlCase advises your development teams during remediation, re-tests exploitable findings and issues a closure report, the evidence required by PCI DSS Requirement 11.4.4.

Ready to Test Your Applications?

Book Expert Time
Chat with an Advisor Available now
Chat with our representative
Compliance Advisor
Compliance Advisor HUMAN · LIVE
Online now · Replies within 2 minutes