Assess Once, Comply to Many


Real-World Assurance
Findings are manually validated and exploited rather than reported from a scanner, so your remediation effort goes to issues attackers exploit.

Coverage Beyond the Network Perimeter
Testing addresses access control, session, logic and API weaknesses firewalls, patch management and vulnerability scanning do not detect.

Audit-Ready Evidence
Methodology, scope, findings and re-test closure are documented in the form assessors expect for PCI DSS, ISO 27001, SOC 2, HIPAA and Indian regulatory requirements.

One Compliance Partner
Combine penetration testing with ControlCase compliance and certification programs to reduce duplicated effort and evidence collection across audits.
What is Application Penetration Testing?
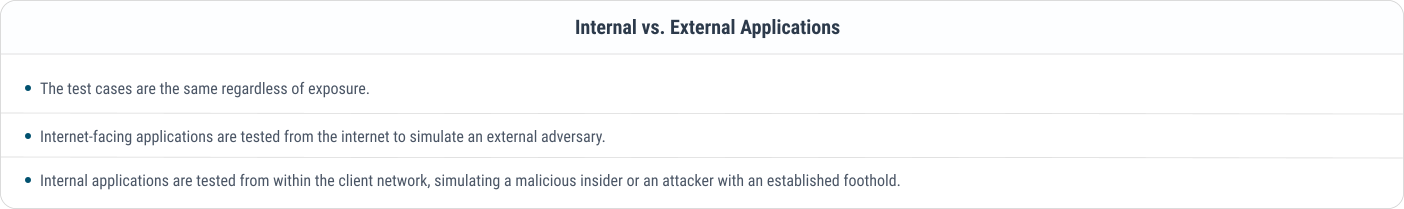
Independent application testing is a requirement under most security standards and regulations. PCI DSS v4.0.1 Requirements 11.4.1 to 11.4.4 call for a defined penetration testing methodology, internal and external penetration testing at least once every 12 months and after significant change, and correction and re-testing of exploitable findings. ISO/IEC 27001:2022, HIPAA and HITRUST, SOC 2, GDPR, the India DPDP Act 2023, and RBI, SEBI CSCRF and CERT-In requirements set comparable expectations.
What We Test
- Web applications: Traditional server-rendered applications, single-page applications, admin and back-office consoles, customer and partner portals.
- APIs and web services: REST, SOAP, GraphQL and gRPC interfaces, including undocumented, versioned and machine-to-machine endpoints.
- Mobile applications: Android and iOS clients, covering the application binary, local data storage, platform interaction and supporting backend services.
- Thick client and desktop: Client-server and installed desktop applications, including local privilege, storage and traffic interception testing.
- Cloud-native workloads: Application-layer testing of containerized and serverless services, including exposed management interfaces and inter-service authorization.
- AI and LLM-enabled features (optional): Prompt injection, insecure output handling, excessive agency and data leakage in applications with integrated language models.
Why Choose ControlCase for Application Penetration Testing?
Testing Perspectives
The approach is agreed during scoping and usually combines the perspectives below. Every engagement uses automated tooling for coverage and manual testing for exploitation, chaining and business logic.
Description: No prior knowledge of the application, its architecture or its deployment.
Key areas: Discovering and attacking the application from the outside.
Applies to: Simulating an unauthenticated external attacker.
Description: Valid credentials for each application role, plus basic architecture and platform information.
Key areas: Authenticated attack surface, horizontal and vertical privilege escalation, and business logic flaws.
Applies to: Most engagements. This is the recommended default.
Description: Credentials plus design documentation, API specifications and, where agreed, source code access.
Key areas: The deepest coverage and the most precise remediation guidance.
Applies to: Engagements where design documentation, API specifications or source code are available.
ControlCase Application Penetration Testing Process